2025 Performance Highlights (G)
- There were no cases of customer privacy violations.
- In 2025, information usage management audits identified a total of eight recommendations for improvement. Personal data protection audits were also conducted for six outsourced contractors, resulting in five recommendations for improvement.
- TIPC has incorporated cybersecurity requirements into its model contracts to manage cybersecurity risks in leased areas.
- Obtained ISO 27001:2022 certification through independent third-party verification.
- The Chief Cybersecurity Officer chaired one management review meeting, during which all established indicators for measuring the effectiveness of the ISMS (IS-TW-04-003) were met.
- Operational Technology (OT) system administrators and their immediate supervisors attended the “Joint Course on Competency Mapping for Industrial Control Systems (ICS) Cybersecurity in the Transportation Sector.” A total of 53 participants attended the course, all of whom received certification, representing a 100% certification rate.
- No incidents involving data breaches, theft, or loss of customer information were reported among the issues raised at the port business forums.
- No major customer complaints were received from shipping lines. A total of 11 forums were held, during which 19 safety-related issues were addressed.
- Marketing Incentive Platform Upgrade: The platform’s technical architecture was enhanced to ensure seamless access from both mobile devices and desktop computers. By digitizing the incentive application process, the upgrade improved information transparency and administrative efficiency while significantly enhancing the user experience.
- TPnet: In response to government policy and the latest regulatory requirements, the E-Invoice Message Implementation Guideline (MIG) was upgraded to Version 4.1.
- According to the 2025 Gender-Friendly Environment Satisfaction Survey for Port Passenger Terminals and Customs Clearance Service Stations, the average overall passenger satisfaction score was 4.47 out of 5.
Comply with the SDGs
- SDG9【SDG 9.c】
- SDG17【SDG 17.17】
Management Policy
Covered material topics
- Information Security and Customer Privacy
- Customer Service Quality
Policy
- Information Structure
- Customer Service and Feedback Management
Management Evaluation System
- Cybersecurity Management
- Customer Service and Feedback Management
Information Structure
TIPC respects customer privacy and complies with the Personal Data Protection Act, promulgated in 2023, and the Cyber Security Management Act, promulgated in 2018, in the collection, processing, and use of customer data. TIPC continues to strengthen its cybersecurity protection and defense capabilities by establishing a comprehensive cybersecurity policy, appointing a Cybersecurity Officer, and establishing a Cybersecurity Management Committee.
In addition, the Company obtained certification to the revised ISO 27001:2022 standard in 2024. Through the implementation of the ISO 27001 international information security standard, TIPC continues to enhance its information security management system and effectively implement internal control mechanisms to fulfill its responsibility to protect customer privacy. The Company’s information security status is reviewed regularly and reported to the President on a quarterly basis and to the Board of Directors on a semiannual basis.
Information Security Policy
-
Implementation of program management
-
Regulatory Compliance
-
Prevention is more important than response
-
Ensure information security
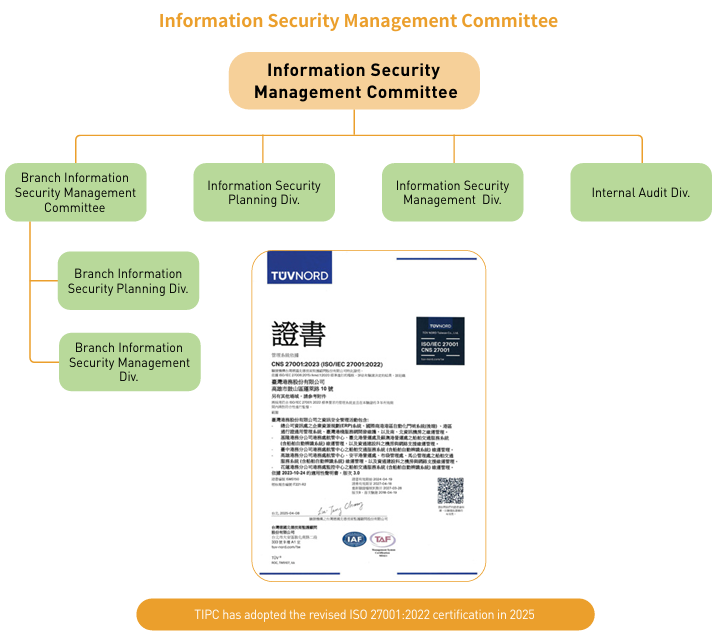
Information Security Management Committee
Cybersecurity Management
TIPC conducts internal and external audits annually in accordance with the ISO 27001 standard. The Chief Cybersecurity Officer convenes the Cybersecurity Management Committee and chairs an annual management review meeting to assess the implementation of information security performance indicators and establish targets for the following year, thereby ensuring the continuous improvement of the information security management system.
As a specific non-government agency subject to the Cyber Security Management Act, TIPC is required to comply with the Act’s provisions. Violations of Article 20 or 21 may result in fines imposed by the Ministry of Transportation and Communications. To reduce cybersecurity risks, TIPC has incorporated relevant cybersecurity requirements into its lease agreement template since 2022 to strengthen lessees’ cybersecurity responsibilities.
Annual cyber security risk assessments are conducted. In response Annual cybersecurity risk assessments are conducted. In response to the digitization of customer application and billing processes, TIPC conducts asset inventories and risk assessments in accordance with its Information Security Management System (ISMS) standards, covering the three key aspects of information security: availability, integrity, and confidentiality. For identified risks that exceed acceptable thresholds, risk mitigation plans are developed and implemented to reduce potential impacts and strengthen the protection of customer data and transaction privacy. In 2025, no privacy-related complaints were received, demonstrating the effective implementation of the cybersecurity management system.
TIPC has established Information and Communications Security Terms and Conditions for Outsourcing to provide guidance for the internal procurement of information technology (IT) equipment, software, and services. These terms and conditions clearly specify the information security requirements that suppliers must comply with, including the following:
|
Time of incident |
Countermeasure |
|
Upon becoming aware of a cybersecurity incident, such as a suspected personal data breach |
Notify the Company within the specified timeframe and complete the required response procedures. |
|
When suppliers obtain information while providing support services without prior authorization from the port authority |
Complete the required application form in accordance with applicable requirements. All operations must be accompanied or monitored by a designated representative of the port authority. |
|
When suppliers obtain information while providing support services without prior authorization from the port authority |
Do not disclose the information to any third party. |
| Upon termination or cancellation of the contractual relationship between the two parties |
Suppliers shall confirm that all data retained for the performance of the contract has been returned, transferred, deleted, or destroyed, thereby ensuring adequate protection of customer privacy. |
The “Global Information Network,” established in accordance with the Company’s privacy policy, provides visitors with secure access to the services and information available on the website. The website protects users’ privacy and does not modify or delete any personal data or files without prior consent, thereby providing visitors with a secure browsing experience.
Cybersecurity Education and Training
TIPC conducts cybersecurity education and training in accordance with the Cyber Security Management Act. In 2025, the Cybersecurity Officer received at least 12 hours of professional cybersecurity training, while other information security personnel received at least three hours of training. General users and supervisors also received an average of three hours of cybersecurity training. In 2025, the training completion rate reached 100%, helping to strengthen cybersecurity awareness and reduce the risk and potential impact of personal data breaches. No substantiated incidents involving customer data breaches, theft, or loss were reported in 2025.
Customer Service and Feedback Management
TIPC adheres to its policy of “enhancing interaction with operators and strengthening policy communication” and continuously improves service quality while safeguarding customer health and safety through systematic tracking and management of customer feedback, robust information security measures, and regular stakeholder forums. In 2025, no material customer complaints were received from shipping lines. TIPC also held 11 forums and addressed 19 customer health- and safety-related issues. According to the 2025 Gender-Friendly Environment Satisfaction Survey for Port Passenger Terminals and Customs Clearance Service Stations, the average overall satisfaction score for passenger terminal facilities was 4.47 out of 5.0.
TIPC places great importance on protecting customer privacy. The collection, processing, and use of customer information are conducted in accordance with the Personal Data Protection Act and applicable information security management requirements. During the reporting year, no incidents involving the leakage or loss of customer data were reported, and the Company continued to update its cybersecurity oversight measures in accordance with guidance from the competent authorities. For digital services related to port operations, including port and terminal applications and billing services, TIPC’s Information Technology Department and Information Security Management Committee establish cybersecurity policies and implement corresponding management mechanisms to safeguard customer transaction data and personal information.